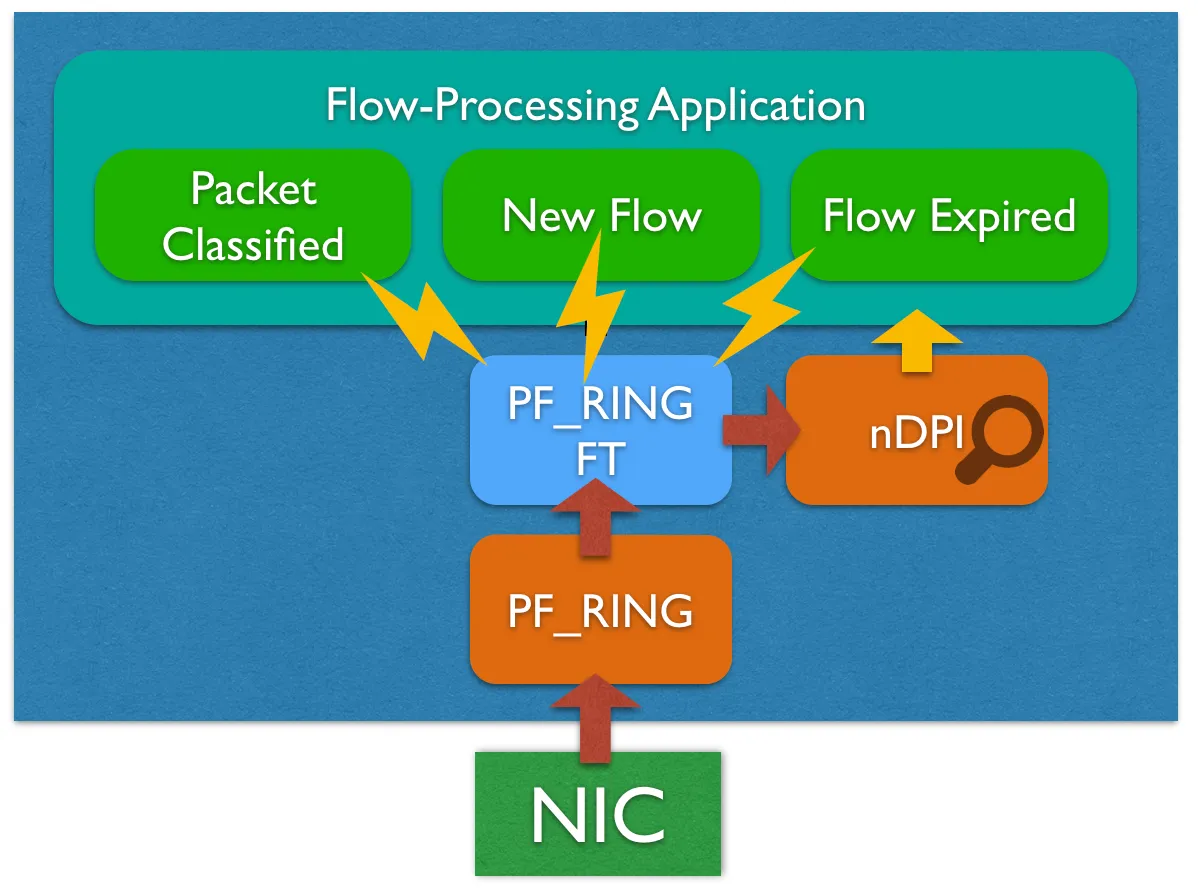
This is to announce a new PF_RING major release 7.4. This release includes many improvements to the PF_RING FT library, which is now more mature thanks to new API functionalities and features…
This is to announce the release of nDPI 2.6. Several dissectors have been improved and a few new ones have been added, as well we have improved the detection logic (this in…
Last Friday Oct 26th, at the University of Pisa we have celebrated 20 years of ntop open source code development and hacking culture. It has been a success with over 110 registered…
ntopng can be used to visualize traffic data that has been generated or collected by nProbe. Using ntopng with nProbe is convenient in several scenarios, including: The visualization of NetFlow/sFlow data originated…
This is a message for the Italian speaking community willing to attend our 20 years of ntop workshop that will take place in Pisa, Italy, where ntop was born. If there is…
ntopng 3.6 release is paving the way to metrics-based traffic analysis. We have finally put ntopng on top of a timeseries-independent layer that allowed us to currently RRD and InfluxDB and in…
While tools like github and mailing lists can serve developers and experts, sometimes people look for a quick help. For this reason we have create a new Telegram group called @ntop_community that…
Last week we have presented two tutorials at the Sharkfest US 2018 edition: sFlow: Theory and practice of a sampling technology [ slides ] Packet monitoring in the days of IoT and…
Yesterday our friends at InfluxData organised a meetup at their HQ in San Francisco, CA. For all those who have been unable to attend the event, these are the presentation slides so…
This is to announce a new PF_RING major release 7.2 that includes: Support for Ubuntu 18 as well the latest Debian and CentOS kernels. Many improvements to the FPGA capture modules and…
Hi all, this is to invite all of your to the How ntop built their high-speed Web-based traffic analysis and flow collection with the use of InfluxDB webinar, organised by our friends…
Motivation Most network monitoring and security applications are based on flow processing, which is in practice the activity of grouping packets based on common attributes (e.g. source and destination IP, source and…