
Community (Open Source)
Free
- Reatime visibility and top talkers
- Layer-7 application detection
- Historical timeseries for hosts
- VLAN, OS, Country and AS stats
- Alerts and notifications
- Active monitoring and network discovery
High-Speed Web-based Traffic Analysis and Flow Collection
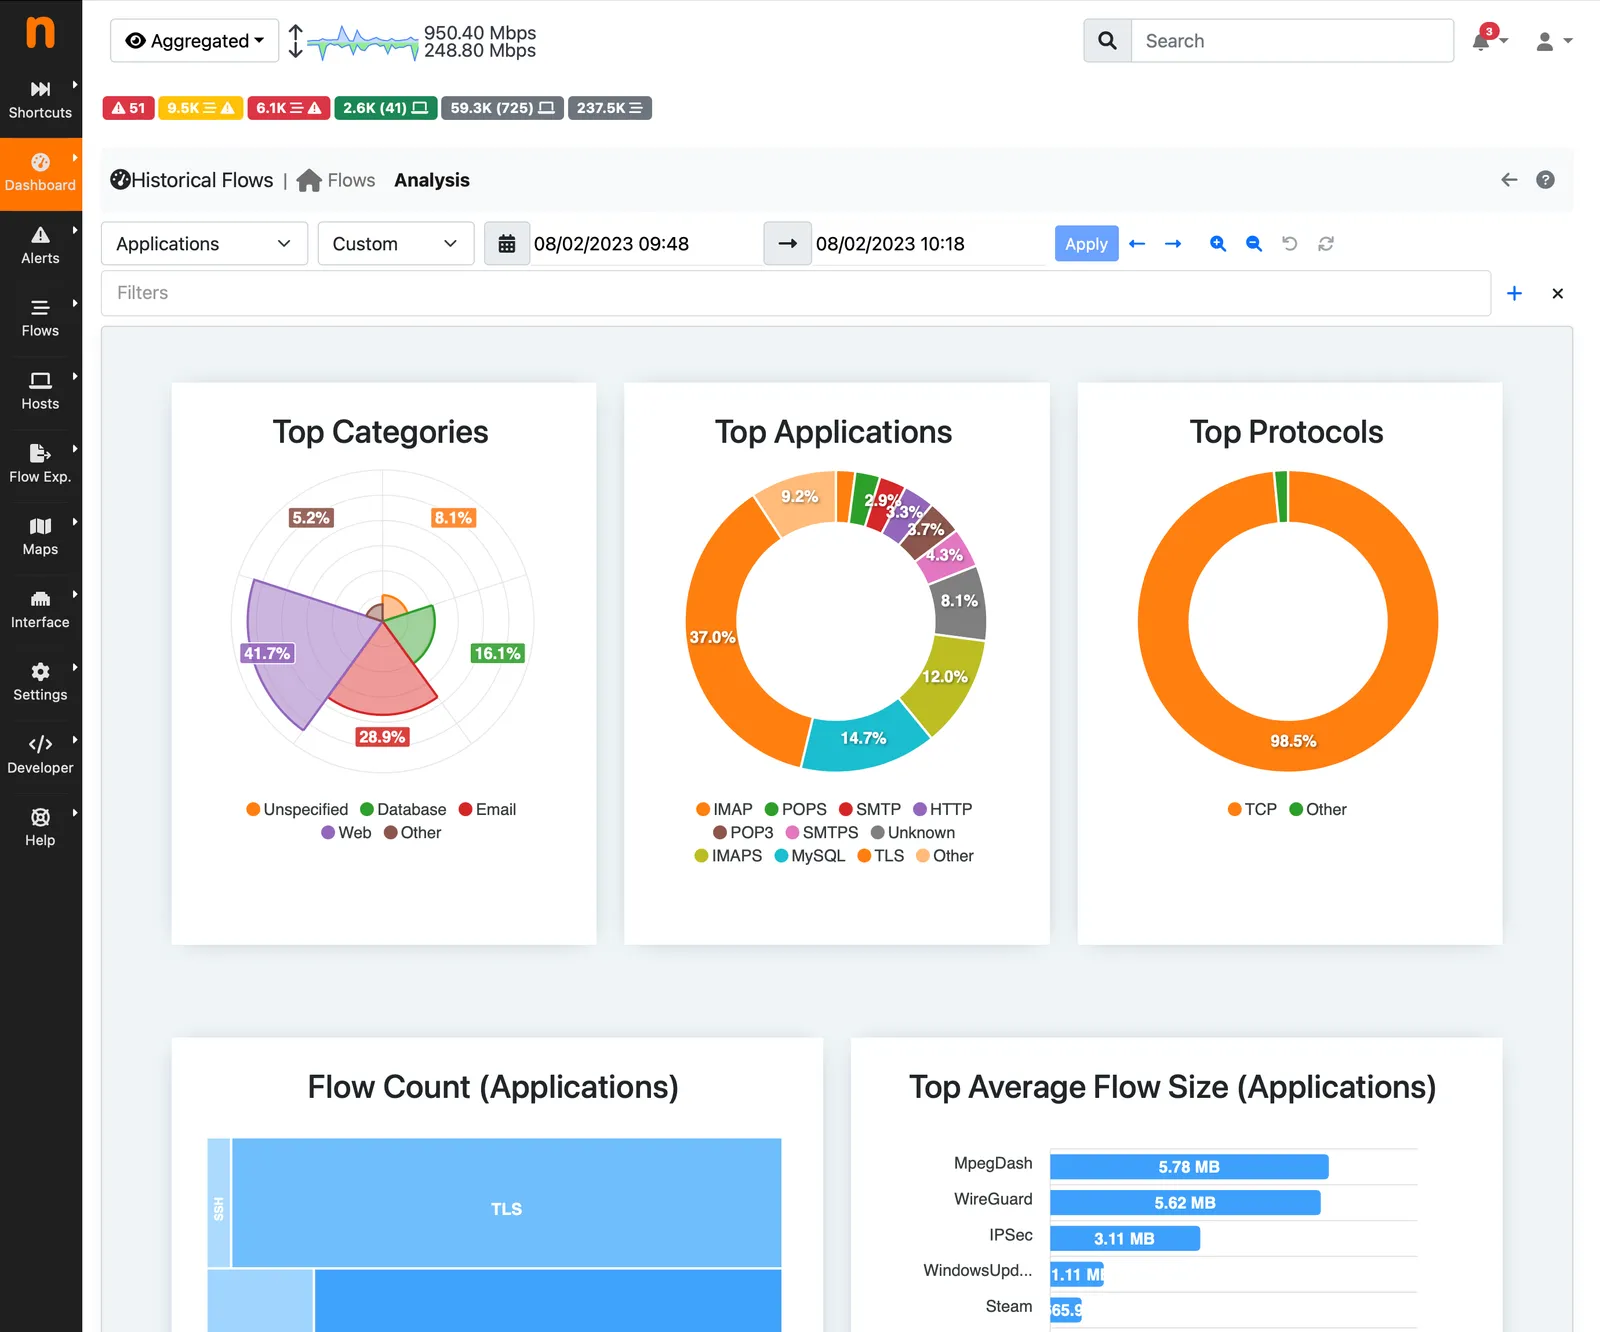
ntopng is for network and security teams that want one web interface for real-time and historical traffic visibility. It reads packets from a mirror port or TAP, flows from NetFlow and sFlow exporters (through nProbe), SNMP devices, firewall logs and IDS events. Choose it when you want to see who talks to whom, with which application, and how well, without stitching several tools together.
Monitor hundreds of thousands of hosts with zero‑delay traffic analysis on high‑speed uplinks.
Flow collection requires ntopng to be used in conjunction with nProbe which can act as probe/proxy.
The communication between nProbe and ntopng takes place over ZeroMQ, a publish-subscribe protocol that allows ntopng to communicate with nProbe.
A remote nProbe is physically monitoring a mirror from a NIC and sending monitored flows to ntopng, or is collecting NetFlow v5/v9/IPFIX or sFlow from one or more exporters (routers or switches). nProbe Cento allows you to monitor even 100 Gbit links when processing packets from a mirror port, yet providing application protocol information by running nDPI.
Mirror (SPAN) ports or TAP devices allow network monitoring tools to observe all packets flowing through the network for for network visibility, troubleshooting, threat detection, and capacity planning, without generating traffic or altering the data path.
A physical NIC card connected to a mirror can be monitored by ntopng itself by simply specifying its interface name. This configuration can be used to monitor a mirror port from a switch, or in conjunction with a TAP device by aggregating two directions from two network interfaces. Alternatively, it is possible to use ntopng in combination with nProbe or nProbe Cento to scale up to 100 Gbit.
Combine L7 visibility, IDS integration, syslog ingestion and alerts for full awareness. ntopng, in addition to behavioral checks able to detect traffic anomalies, can ingest events from IDS systems like Suricata enriching traffic analytics with security insights for faster threat detection and response.
Same criteria for each option: role, when to choose it, limits and cost.
ntopng works even better in distributed networks or high-speed links when paired with nProbe or nProbe Cento!
Try ntopng on your own traffic.
Did you already install the software?
InstallSelect the ntopng version that fits your needs. Different versions unlock different features and capacity.
Check the comparison table for the features set about the various versions.
Free
Pricing in the ntop shop
Pricing in the ntop shop
| Item | Small Network | Medium Network | Large Network |
|---|---|---|---|
| Traffic | 100 Mbps | 1 Gbps | 10 Gbps and above |
| Processor | 2 cores | 4 cores | 8+ cores |
| Memory | 2 GB | 4 GB | 16+ GB |
For further information please check the Hardware Sizing notes.
ntopng Community is distributed under the GNU GPLv3 license. Professional and Enterprise versions are subject to the EULA terms as well.
Monitor hundreds of thousands of hosts with zero‑delay traffic analysis on high‑speed uplinks.
Flow collection
requires ntopng to be used in conjunction with nProbe which can act as probe/proxy.
The communication between nProbe and ntopng takes place over ZeroMQ, a
publish-subscribe protocol that allows ntopng to communicate with nProbe.
A remote nProbe is physically
monitoring a mirror from a NIC and sending monitored flows to ntopng, or is collecting NetFlow v5/v9/IPFIX or sFlow
from one or more exporters (routers or switches). nProbe Cento allows you to monitor even 100 Gbit links when processing packets from a mirror port, yet providing application
protocol information by running nDPI.
Mirror (SPAN) ports or TAP devices allow network monitoring tools to observe all packets flowing through the network for for network visibility, troubleshooting, threat detection, and capacity planning, without generating traffic or altering the data path.
A physical NIC card connected to a mirror can be monitored by ntopng itself by simply specifying its interface name. This configuration can be used to monitor a mirror port from a switch, or in conjunction with a TAP device by aggregating two directions from two network interfaces. Alternatively, it is possible to use ntopng in combination with nProbe or nProbe Cento to scale up to 100 Gbit.
Combine L7 visibility, IDS integration, syslog ingestion and alerts for full awareness. ntopng, in addition to behavioral checks able to detect traffic anomalies, can ingest events from IDS systems like Suricata enriching traffic analytics with security insights for faster threat detection and response.
The Community edition is free. See the ntop shop for pricing. Licenses are perpetual and include one year of maintenance, updates and support. See the pricing page.
The Community edition of ntopng is free and open source under the GNU GPLv3 license. Professional and Enterprise editions are commercial, see the pricing page.
ntopng runs on Linux, FreeBSD, Windows x64 (including Windows 10 and 11), macOS and Raspberry Pi OS.
No. ntopng captures traffic from mirror ports and TAPs with libpcap or PF_RING. To collect NetFlow and sFlow from routers and switches, use nProbe as probe and proxy.
ntopng uses nDPI, the ntop deep packet inspection library, to detect hundreds of Layer-7 protocols, including encrypted traffic.
Download the free Community edition, compare editions and buy in the shop, or talk to the ntop team about your requirements.