nScrub

nScrub

On-Premise Software-Based DDoS Mitigation

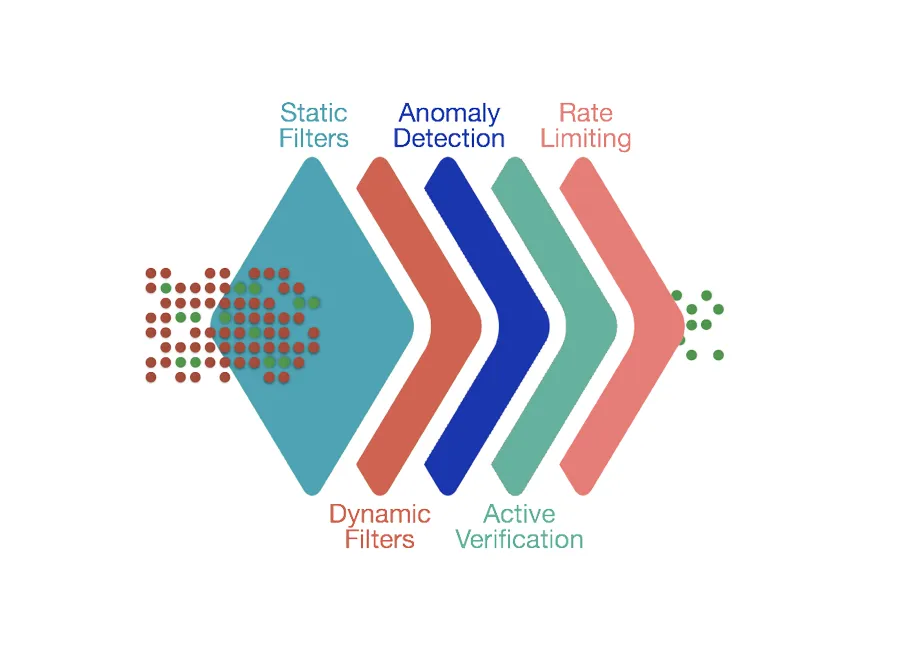
Mitigation layers
10+ Gbit
line rate
Terabit
scalable architecture
BGP
diversion or bridge mode

Who should choose nScrub

nScrub is on-premise, software-based DDoS mitigation. Choose it when you want to filter attacks inside your own infrastructure, as a transparent bridge or as a router with BGP diversion, on commodity hardware.

  • You want mitigation on your premises and not a cloud scrubbing service.
  • You need to start at 10+ Gbps and scale towards Terabit/s with a modular design.
  • You serve several customers or networks and need separate mitigation profiles.

Ideal use case for nScrub

Environment
ISP, data center and enterprise networks. Bridge mode needs no routing changes, router mode works with BGP diversion.
Team
network operators who manage mitigation policies through web UI and REST API.
Technical requirements
4 cores at 3 GHz mitigate 10 Gbps at line rate, and performance scales with more cores. Hardware bypass is available for always-on setups.
Problem solved
multi-layer enforcement, session verification, blacklists, rate limiting, signatures and anomaly detection.

Deployment scenarios

  • On-Demand Traffic Diversion and Mitigation

    When operating in routing mode, nScrub offers the ability to dynamically divert and mitigate traffic on demand during a DDoS attack. Rather than permanently rerouting all traffic through the mitigation infrastructure, nScrub allows selective steering of suspicious or attack-bound flows only when necessary. BGP is a common option used to implement this. This targeted approach ensures minimal latency impact during normal operations, while providing rapid, efficient protection when under threat. By integrating seamlessly into existing network topologies, nScrub in routing mode enables flexible, on-demand traffic diversion, keeping your services online and your mitigation costs under control.
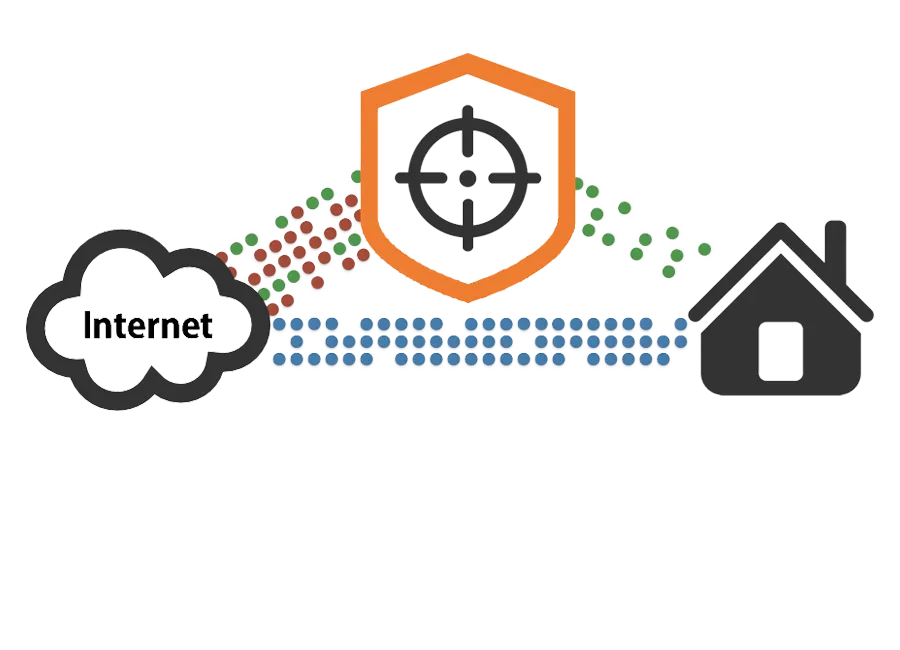
    nScrub BGP traffic diversion
  • Auto Mitigation Engage with Transparent Bridge

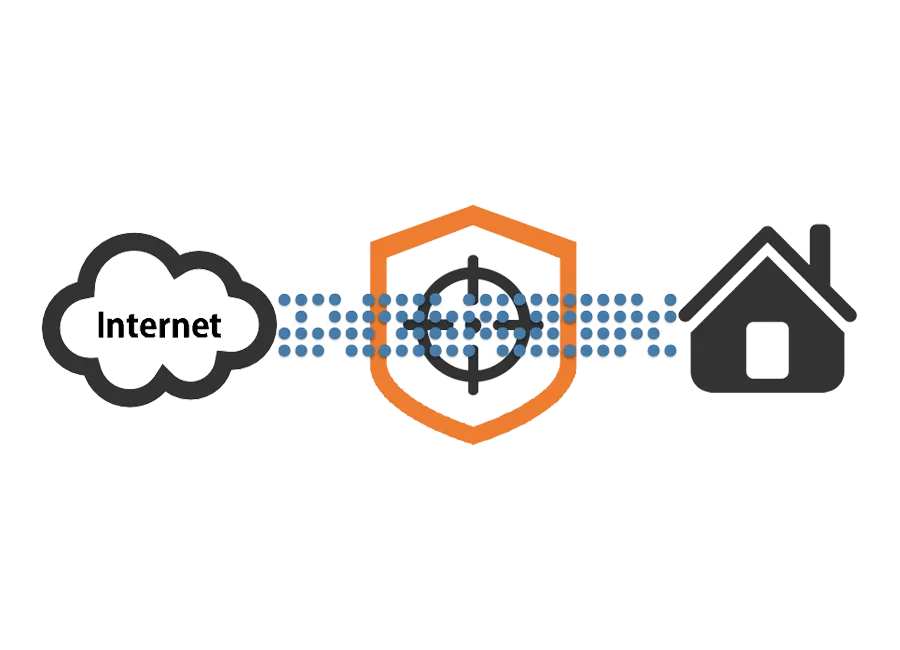
    Running nScrub in transparent bridge (Bump-In-The-Wire) mode offers seamless, zero-configuration DDoS protection. Deployed inline, nScrub forwards all traffic untouched under normal conditions, with no need for traffic diversion or routing changes. When an attack is detected, mitigation is automatically engaged, filtering malicious traffic in real time while allowing legitimate flows to pass through uninterrupted. This mode provides always-on protection with minimal operational complexity, making it ideal for environments where simplicity and reliability are critical. 
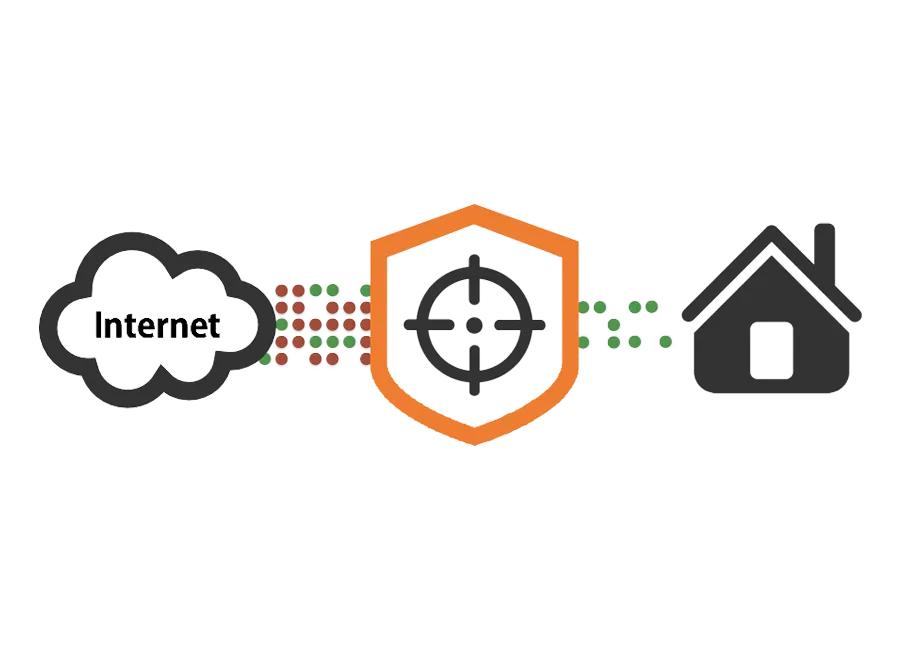
    nScrub transparent bridge deployment
  • Always-On Reliable Mitigation with Hardware Bypass

    In environments where uptime is paramount nScrub can be deployed in transparent bridge mode combined with hardware bypass for maximum reliability and zero disruption. In this setup, nScrub operates inline as a bump-in-the-wire device, inspecting and forwarding traffic without modification under normal conditions. When a DDoS attack is detected, mitigation is instantly and automatically engaged, blocking malicious traffic in real time. If the system experiences a power failure or software crash, the hardware bypass ensures uninterrupted traffic flow, allowing packets to continue passing through without delay or loss. This configuration offers the following key advantages:

    • No configuration required: plug-and-play setup with no need for routing changes or traffic diversion
    • Always-on protection: automatic mitigation only when needed
    • Fail-safe operation: hardware bypass guarantees network continuity, even in failure scenarios.

    With this approach, organizations can achieve robust, transparent DDoS defense with the highest levels of operational reliability.
    nScrub bypass mode
  • Multi-Tenancy Support for Heterogeneous Networks

    When deployed in heterogeneous networks, nScrub multi-tenancy support can be used to define multiple mitigation profiles active concurrently on the same instance, by defining multiple destinations. How this works:
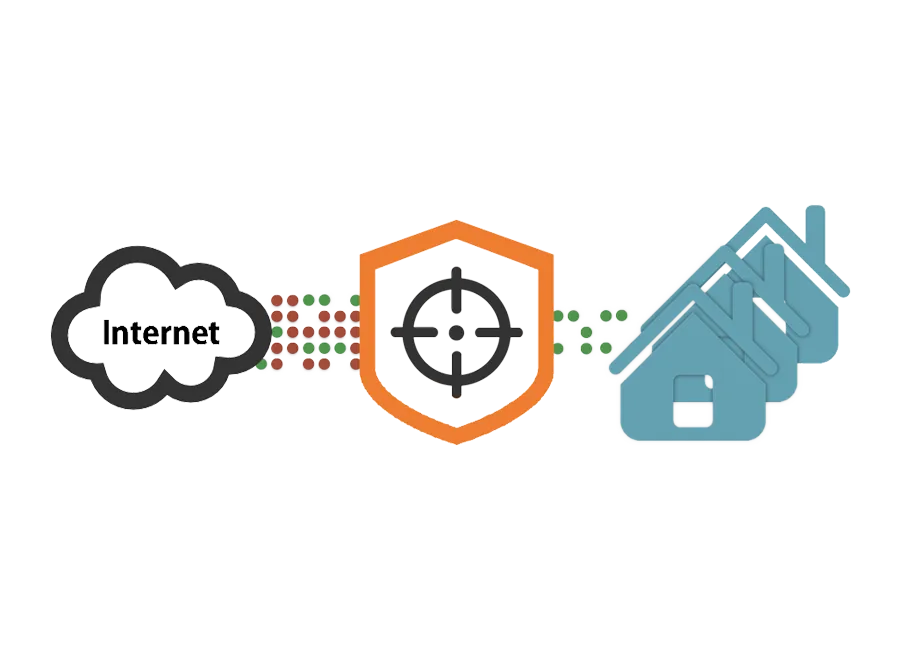
    • Ingress traffic is split towards several virtual mitigators, based on the destination IP address, this way it is possible to specify traffic enforcement policies per destination subnet
    • Each virtual mitigator is bound to traffic enforcement profiles: default, white, black, gray. Each profile contains a traffic enforcement configuration (e.g. SYN check=yes, ICMP Drop=No) and applies to source IPs according to the lists (white/black/gray).
    • Global or per-destination bypass mode is supported, to handle maintenance or exclude a target
    nScrub multitenancy

nScrub alternatives, compared

Same criteria for each option: role, when to choose it, limits and cost.
  • Bridge mode

    • Role: Inline, transparent.
    • Choose it when: Zero-configuration protection and automatic engagement when an attack is detected.
    • Limits: Inline device; use hardware bypass for maximum uptime.
    • Cost: same license
  • Router mode with BGP

    • Role: Traffic is diverted on demand.
    • Choose it when: You want to steer only attack-bound traffic.
    • Limits: Needs BGP and routing design.
    • Cost: same license

When nScrub is not the right choice

  • It is a software product: you provide the hardware and the capacity for your attack size.
  • It runs on your hardware: the capacity you get depends on the cores you provide.
  • Policy design takes network knowledge. Plugins in C extend checks if needed.
  • See the ntop shop for pricing.

Key Features

  • Multi-layer traffic enforcement
  • Active sessions verification for protocols including TCP and DNS
  • Flexible subnet blacklists and whitelists
  • DNS check, force DNS over TCP
  • ACL-like policies based on UDP/TCP/ICMP fields
  • Signature-based filtering, HTTP requests filtering
  • Anomaly detection based on traffic behavior
Show 5 more
  • Rate limiting based on source, destination, protocol
  • Plugins support to load custom checks and validate additional protocols
  • Multi-tenancy support with configuration of multiple mitigation profiles by destination
  • Web-based UI with historical graphs and statistics
  • PCAP dump on request triggered by an event-driven scriptable engine
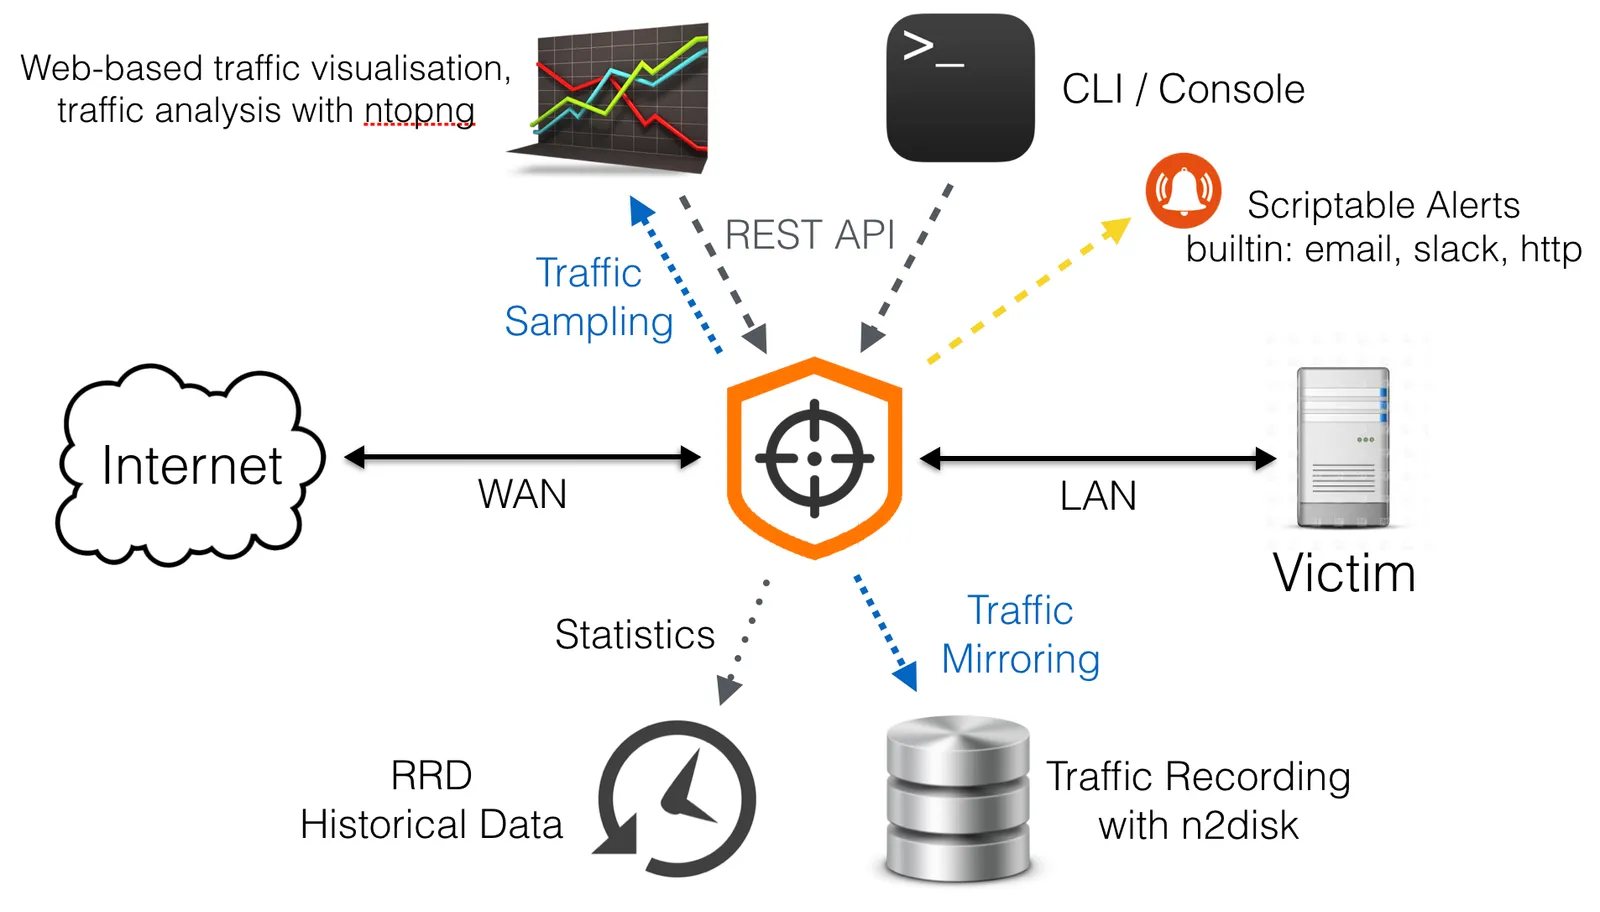
nScrub architecture

Try nScrub on your own traffic.

Tech Specs

Platforms

  • Linux

UI/API

  • Web GUI available through any HTML5-ready browser with traffic statistics and engage information
  • HTTP-based RESTful API for configuring the mitigation policies
  • TLS/HTTPS support
  • Plugins support (C)

Requirements

nScrub required 4-cores 3Ghz to mitigate 10 Gbps line-rate. Performance scale increasing the number of cores.

Protocols

  • Ethernet/VLAN
  • IPv4/IPv6
  • TCP/UDP/ICMP
  • GRE

DOCS

Choose Your Model

Did you already install the software?

Install

Select the model. Different models unlock different features and capacity. Check the comparison table.

S/M/L/XL/XXL

Pricing in the ntop shop

  • Multi-layer traffic enforcement and sessions verification
  • Routing mode
  • Transparent bridge mode
  • Hardware bypass support
  • Multi-tenancy support

    Frequently asked questions

    On-Demand Traffic Diversion and Mitigation

    When operating in routing mode, nScrub offers the ability to dynamically divert and mitigate traffic on demand during a DDoS attack. Rather than permanently rerouting all traffic through the mitigation infrastructure, nScrub allows selective steering of suspicious or attack-bound flows only when necessary. BGP is a common option used to implement this. This targeted approach ensures minimal latency impact during normal operations, while providing rapid, efficient protection when under threat. By integrating seamlessly into existing network topologies, nScrub in routing mode enables flexible, on-demand traffic diversion, keeping your services online and your mitigation costs under control.

    nScrub BGP traffic diversion
    Auto Mitigation Engage with Transparent Bridge

    Running nScrub in transparent bridge (Bump-In-The-Wire) mode offers seamless, zero-configuration DDoS protection. Deployed inline, nScrub forwards all traffic untouched under normal conditions, with no need for traffic diversion or routing changes. When an attack is detected, mitigation is automatically engaged, filtering malicious traffic in real time while allowing legitimate flows to pass through uninterrupted. This mode provides always-on protection with minimal operational complexity, making it ideal for environments where simplicity and reliability are critical. 

    nScrub transparent bridge deployment
    Always-On Reliable Mitigation with Hardware Bypass

    In environments where uptime is paramount nScrub can be deployed in transparent bridge mode combined with hardware bypass for maximum reliability and zero disruption. In this setup, nScrub operates inline as a bump-in-the-wire device, inspecting and forwarding traffic without modification under normal conditions. When a DDoS attack is detected, mitigation is instantly and automatically engaged, blocking malicious traffic in real time. If the system experiences a power failure or software crash, the hardware bypass ensures uninterrupted traffic flow, allowing packets to continue passing through without delay or loss. This configuration offers the following key advantages:

    • No configuration required: plug-and-play setup with no need for routing changes or traffic diversion
    • Always-on protection: automatic mitigation only when needed
    • Fail-safe operation: hardware bypass guarantees network continuity, even in failure scenarios.

    With this approach, organizations can achieve robust, transparent DDoS defense with the highest levels of operational reliability.

    nScrub bypass mode
    Multi-Tenancy Support for Heterogeneous Networks

    When deployed in heterogeneous networks, nScrub multi-tenancy support can be used to define multiple mitigation profiles active concurrently on the same instance, by defining multiple destinations. How this works:

    • Ingress traffic is split towards several virtual mitigators, based on the destination IP address, this way it is possible to specify traffic enforcement policies per destination subnet
    • Each virtual mitigator is bound to traffic enforcement profiles: default, white, black, gray. Each profile contains a traffic enforcement configuration (e.g. SYN check=yes, ICMP Drop=No) and applies to source IPs according to the lists (white/black/gray).
    • Global or per-destination bypass mode is supported, to handle maintenance or exclude a target
    nScrub multitenancy
    Bridge mode
    • Role: Inline, transparent.
    • Choose it when: Zero-configuration protection and automatic engagement when an attack is detected.
    • Limits: Inline device; use hardware bypass for maximum uptime.
    • Cost: same license
    Router mode with BGP
    • Role: Traffic is diverted on demand.
    • Choose it when: You want to steer only attack-bound traffic.
    • Limits: Needs BGP and routing design.
    • Cost: same license

    Ready to see nScrub on your network?

    Download the free Community edition, compare editions and buy in the shop, or talk to the ntop team about your requirements.