
Is JA4 Now Obsolete?
JA4 is a modern network fingerprinting standard used to identify and profile clients initiating encrypted TLS (Transport Layer Security) connections. JA4 it is the successor to the widely used but now deprecated…
Open source deep packet inspection.
81 articles
Earlier this week we have presented at Sharkfest Europe 2026 a presentation of our work about traffic detection of Stealth VPNs and AI Inference. The presentation addresses the challenges of detecting modern obfuscated network traffic, specifically from stealth VPNs and custom/local artificial intel
CVE-2026-98432 is a critical, 9.8-severity use-after-free (UAF) vulnerability in the Linux kernel’s IPv4 TCP networking stack. It allows an unauthenticated remote attacker to potentially cause system crashes, memory corruption, or execute arbitrary commands with root privileges. From a network stand
Every TCP connection starts with a SYN, and that first packet says a lot about the machine that sent it. The Linux, Windows, macOS and Android stacks each set different flags, choose…
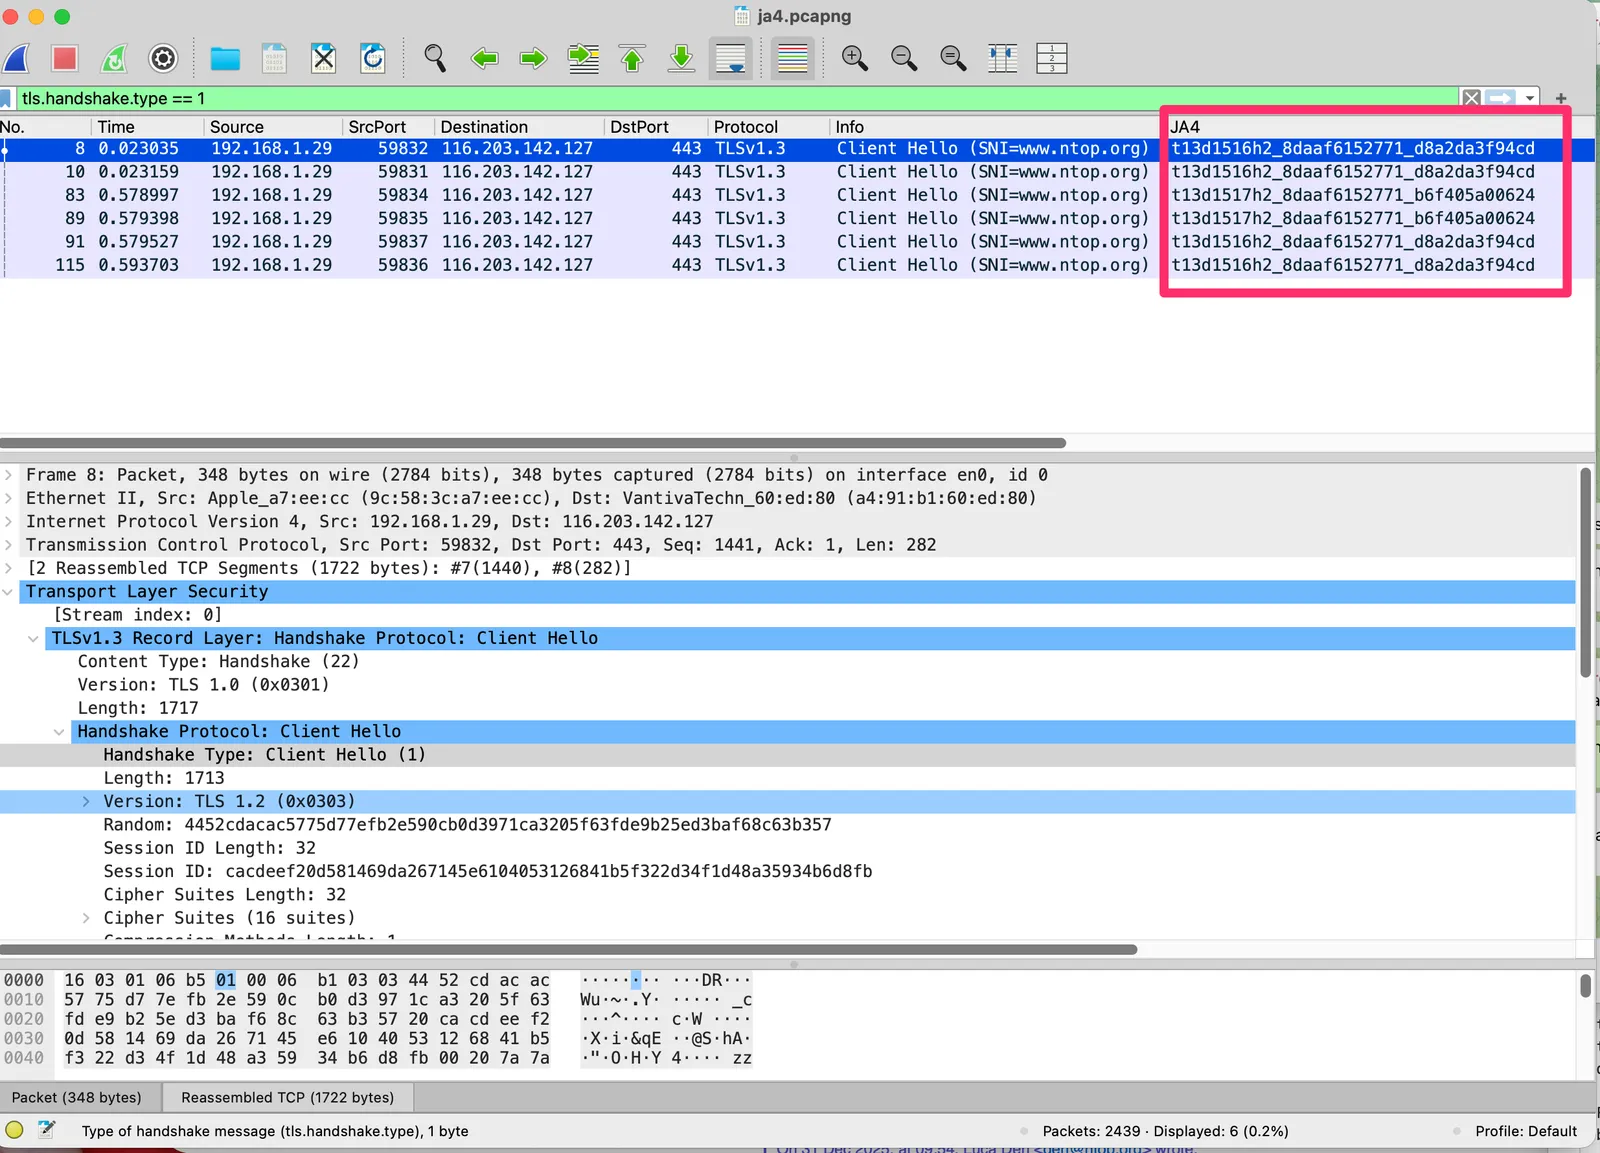
TLS client fingerprinting has become one of the workhorse techniques in network security, and JA4 (FoxIO) has been the de facto standard for identifying TLS clients from their ClientHello messages. But recent…
We are proud to announce the release of nDPI 6.0, the latest major update to our open-source Deep Packet Inspection (DPI) toolkit. This release brings an important licensing update, a brand-new detection…
A License Change for nDPI: Protecting the Project We Started in 2012 When we began nDPI back in 2012, the idea was simple: build an open source, high-performance Deep Packet Inspection engine…
Modern digital security relies on public-key encryption (like RSA and ECC) to protect global data. The future arrival of a Cryptographically Relevant Quantum Computer (CRQC) will completely break these mathematical foundations. To…
by Ivan Nardi One of the recurring challenges when embedding the nDPI library into a production application is answering a deceptively simple question: what is nDPI actually doing right now? You know…
A slow DoS (Denial of Service) attack is a type of cyberattack designed to overwhelm a server or web application by exploiting protocol weaknesses—not through high-volume traffic, but by sending requests very…
JA4 is a modern network fingerprinting standard used to identify and profile clients initiating encrypted TLS (Transport Layer Security) connections. JA4 it is the successor to the widely used but now deprecated…
We are proud to announce the release of nDPI 5.0, the latest major update to our open-source Deep Packet Inspection (DPI) toolkit. This release introduces a powerful new fingerprinting system, unlimited protocol…
SNI (Server Name Indication) is an optional extension in TLS/QUIC that contains the symbolic host name we’re connecting to. For instance, during the TLS handshake, the SNI allows the server to identify…