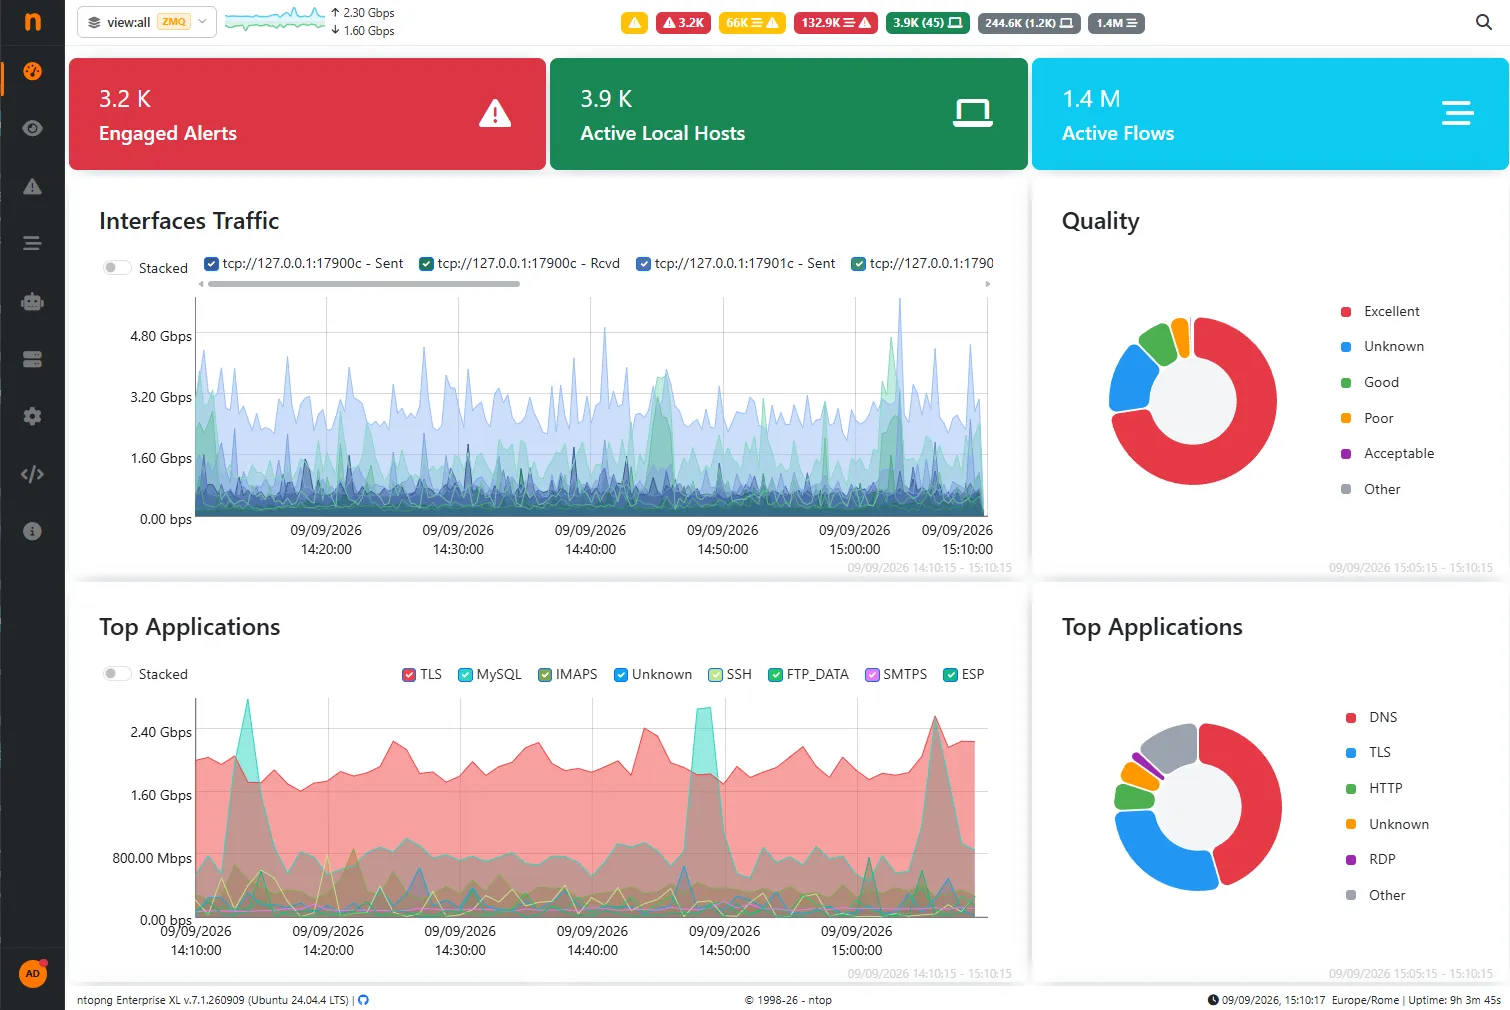
Is your network monitoring keeping pace with AI, larger infrastructures, and the growing need for real observability? We’re excited to introduce ntopng 7.0, alongside new releases of the rest of the ntop…
As network architectures evolve, staying ahead of performance issues and modern cybersecurity threats requires deep visibility and mastery of your tools. Here at ntop, our product range spans from high-speed packet capture…
We are happy to announce that from the latest ntopng dev (6.1) version, ntopng supports exporting data (flows & alerts) to ClickHouse Cloud. Below you can find a step-by-step guide. Quick Start…
The Problem Let’s assume that you have a Network where local hosts generate a constant amount of traffic. How do you find if they are misbehaving? It happens that some local host…
Hello everybody! Welcome back to the weekly blog post of this serie used to update you with the latest ntopng features and graphical changes. Please let us know your feedback! Today we…
In incident analysis it is important to provide evidence of the problem at various level of details: Alerts Alerts are the result of traffic analysis (in ntopng based on checks) that have…
Many of you are asking professional training, in particular in companies and large installations. Over the years we have produced many software applications that allow you to improve network visibility and block…
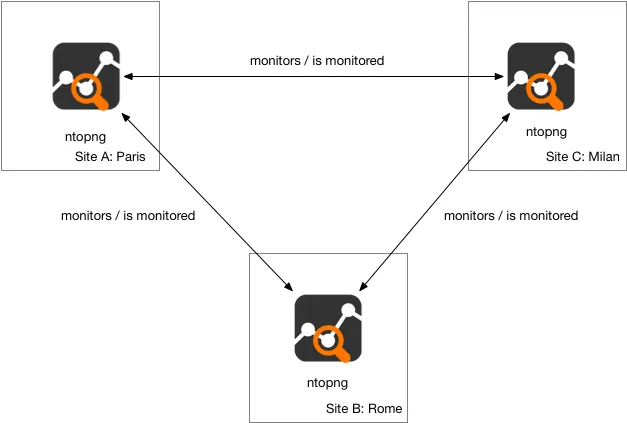
Introduction Quis custodiet ipsos custodes? (Juvenal). In other words: who will guard the guards themselves? If you use ntopng to monitor your network, you also need to make sure ntopng is monitored…
Introduction Recently, we have added Intrusion Prevention System (IPS) capabilities to our nProbe. Those capabilities are available starting from the latest 9.5 version, both for Linux and FreeBSD – including OPNsense and…
We have been receiving several inquiries from pfSense users who would love to complement the classical firewall-style pfSense features with the inline Layer-7-based traffic policing offered by nEdge. Being able place pfSense…
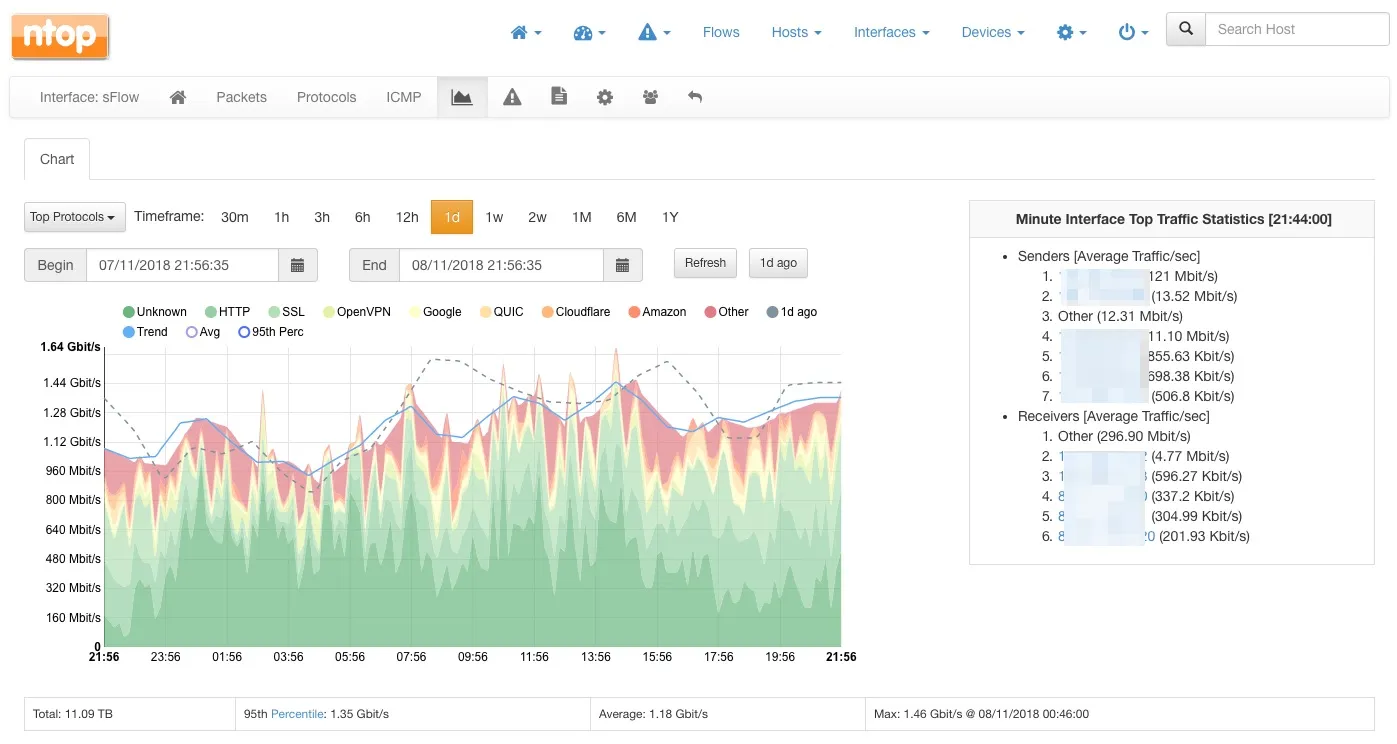
sFlow, short for sampled Flow, is a sampling technology designed to export network devices information, namely: Interface counters (à la SNMP MIB-II); Traffic packets (à la ERSPAN). sFlow agents run on switches,…
Ixia allows to enrich IPFIX records with value-add extensions. Additional information that can be exported, along with standard fields such as source and destination IP addresses, include: Geographical information such as region…