nDPI it is much more than a DPI library used to detect the application protocol. In the past year, nDPI has grown in terms of cybersecurity features used to detect threats and…
At the upcoming Sharkfest Europe 2021 we’ll talk about using Wireshark in cybersecurity. Part of the talk will focus on nDPI and Wireshark integration. Since the last release nDPI features flow risk…
We are proud to announce that a couple of talks have been accepted at FOSDEM 2021, one of the most important FOSS conferences in the world that this yar will take place…
Earlier this month a new highly evasive malware attacker named SunBurst has been disclosed. Immediately some countermeasures have been disclosed and in particular some Snort/Suricata rules have been published. We have analysed…
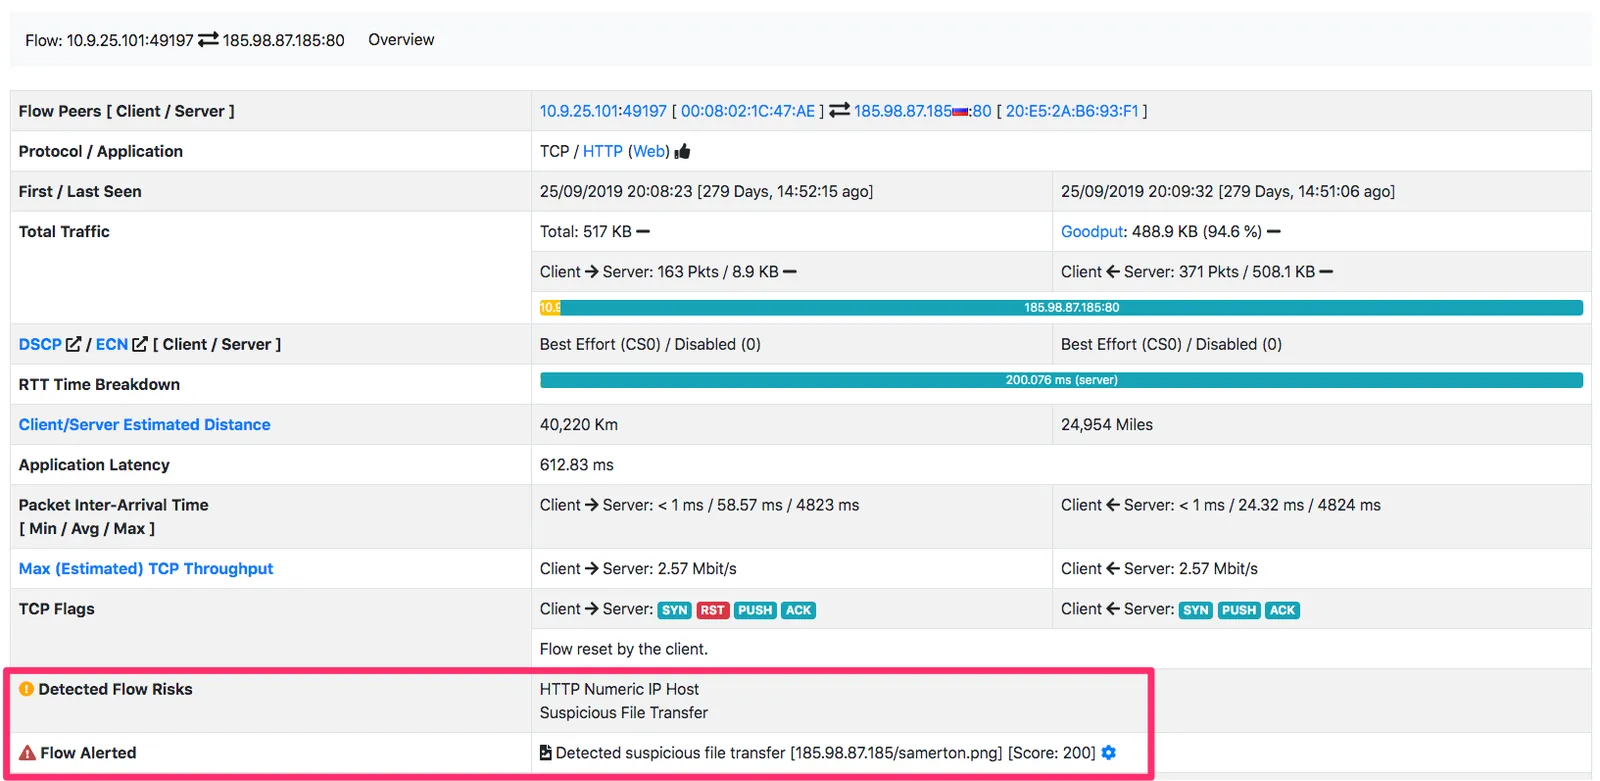
This is to announce the release of nDPI 3.4 that is a major step ahead with respect to 3.2: Detection speed has been greatly optimised Many new functions for statistical protocol analysis…
Most ntop applications (ntopng, nProbe, Cento) and libraries (FT) are based on the concept of flow processing, that merely means keeping track of all network communications. In order to implement this, network…
n2disk is an application that many of the ntop community uses to dump traffic up to 100 Gbit. What few people know is that n2disk can index data not just using packet…
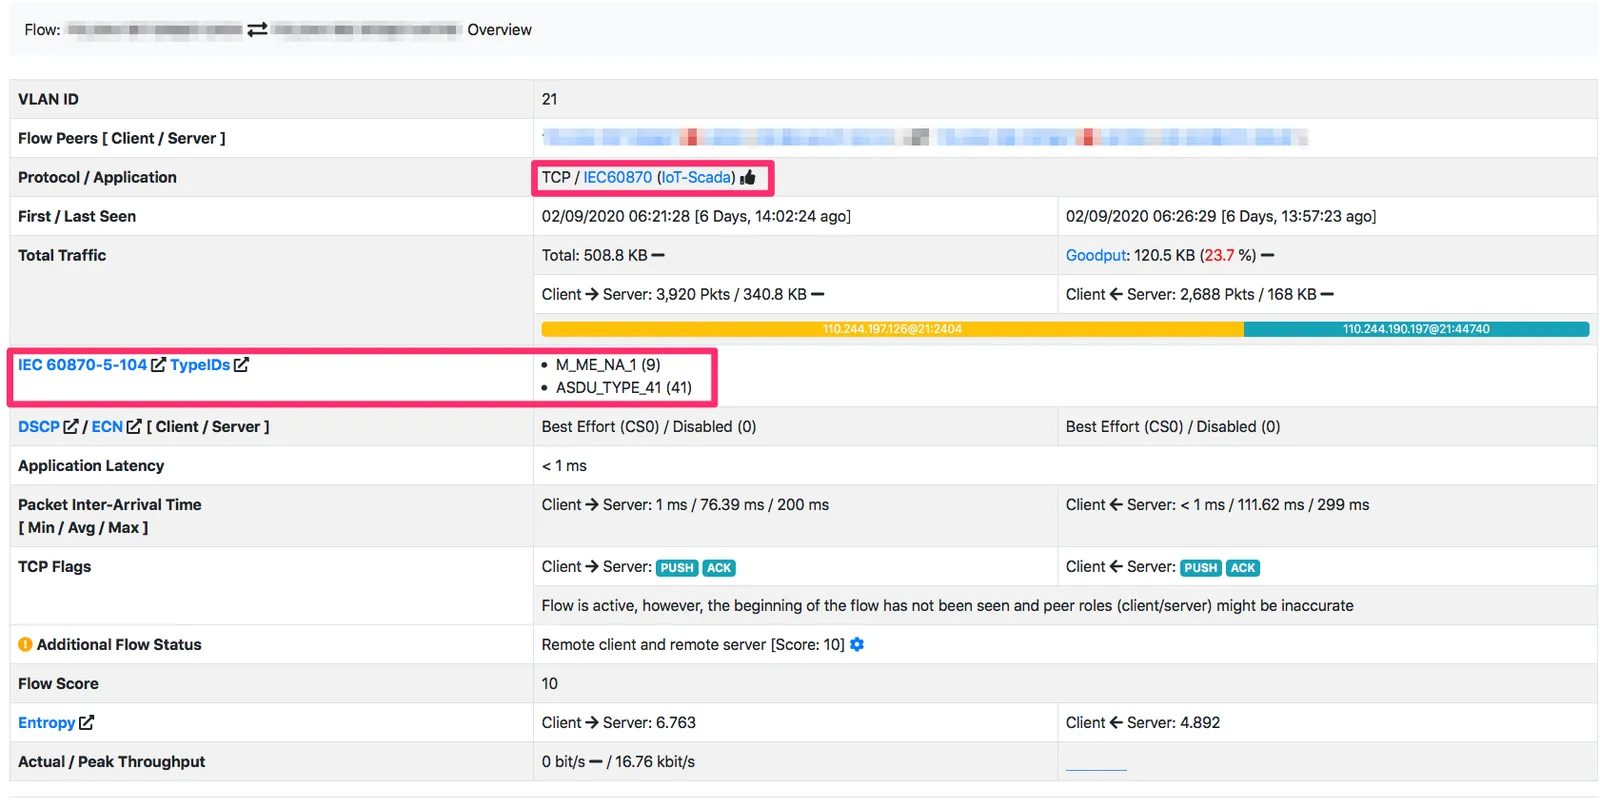
Monitoring Industrial IoT and SCADA traffic can be challenging as most open source monitoring tools are designed for Internet protocols. As this is becoming a hot topic with companies automating production lines,…
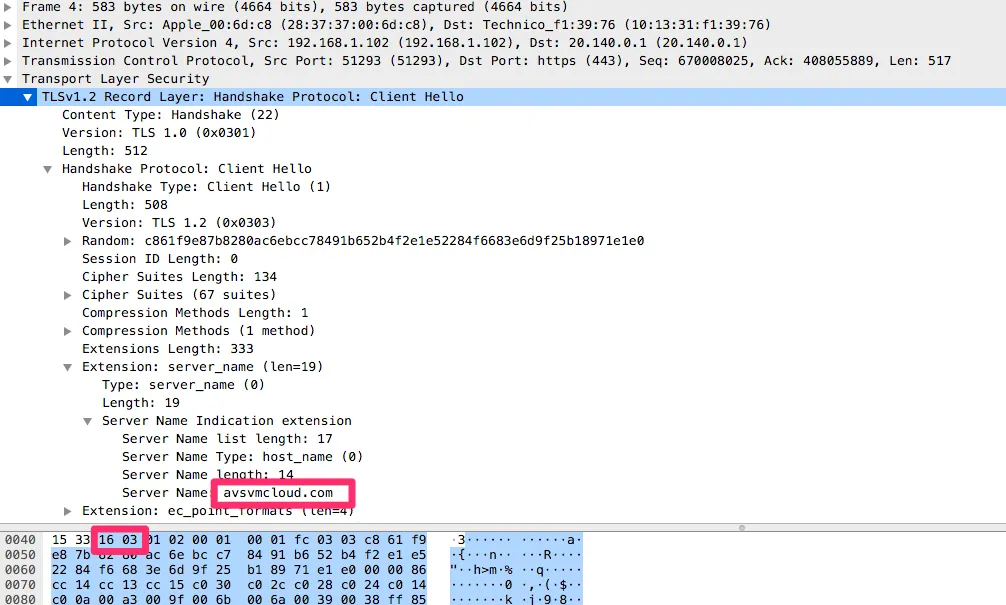
Domain fronting is a technique that was used in 2010s by mobile apps to attempt to bypass censorship. The technique relies on a “front” legitimate domain that basically acts as a pivot…
Earlier last month Ripple20 became popular as it has listed some vulnerabilities found in a custom IP stack used by many IoT devices. Despite the hype on Ripple20, in essence the tool…
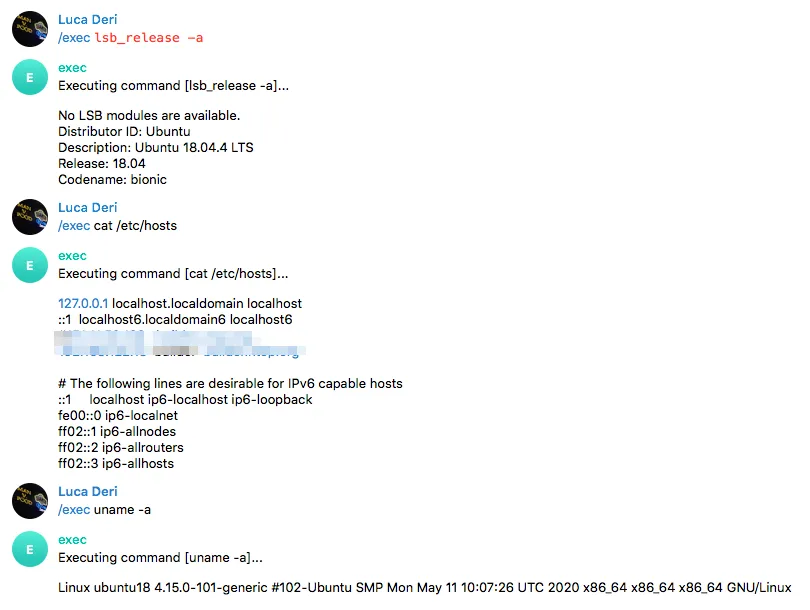
Botnets are a popular way to run malware on a network using the command and control paradigm. Popular protocols used by botnets include IRC and HTTP. Most IDSs can detect bots as…
In the latest nDPI meetup, we have discussed future directions, including extending the current encrypted traffic analysis features. Currently nDPI supports both fingerprint and behaviour encrypted traffic analysis techniques to provide TLS…