
Meet ntop @ Cebit 2012
All those visiting Cebit next week, will have the chance to see what we’re doing at ntop for providing better network monitoring services. We will give a presentation at the Open Source…
708 articles
For years networking companies have used the buzzword zero-copy to qualify those hardware/software solutions that allow applications to play with packets without the need to copy them at all. Zero-copy needs DMA…
All those visiting Cebit next week, will have the chance to see what we’re doing at ntop for providing better network monitoring services. We will give a presentation at the Open Source…
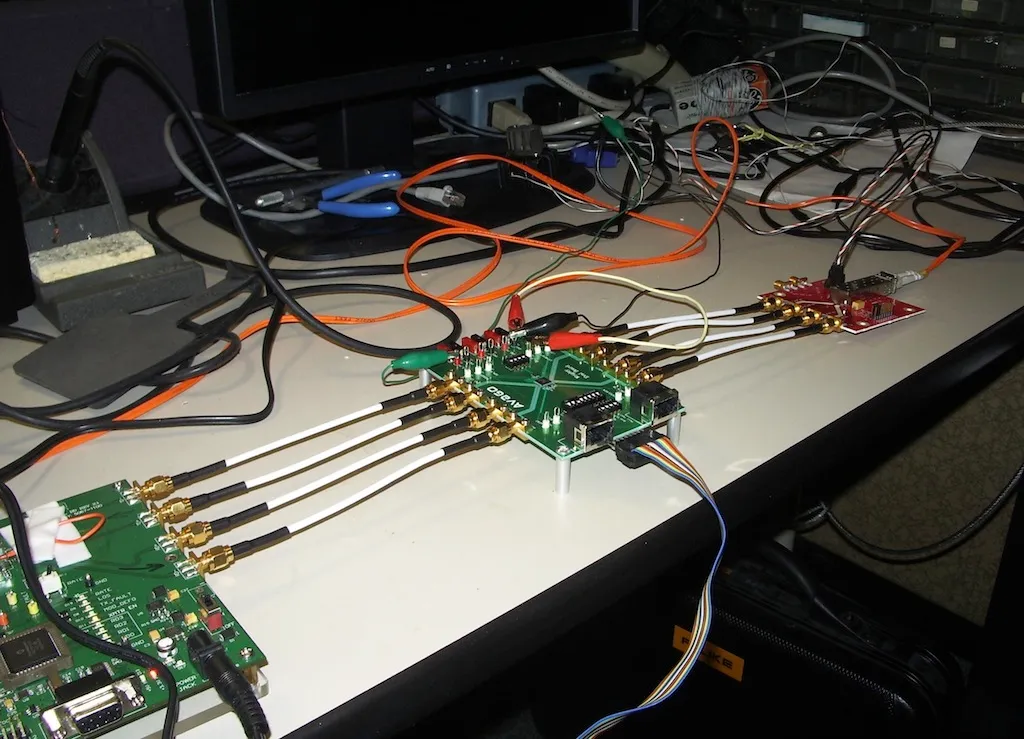
In 2004 my friend Alex Tudor of Agilent involved ntop on a very challenging project. The idea was to monitor the network from the exact place where packets were originated. In fact…
From time to time, Cisco builds ntop-friendly products. This is the time of the Cisco ON100 network agent. This tiny device that can fit on your hand, has been integrated with ntop…
In network monitoring it is very common to use taps for duplicating network traffic (RX and TX directions). Taps are important as they allow network probes to operate passively without interfering with…
The equation “port = (application) protocol” no longer holds. DPI (Deep Packet Inspection) is the way to detect known protocols on non-known ports (e.g. http on ports other than 80) and traffic…
In the past months I have received a few emails about how to position DNA with respect to netmap. To many people they look like two competing solutions, but in reality they…
Most people use nProbe just as a basic NetFlow/IPFIX probe where traffic monitoring is limited to packet header analysis, without further dissecting protocols. This practice is very common inside the NetFlow community…
From time to time the kernel folks are sick and tired of people saying PF_RING is better than what we have upstream, it really isn’t. Fortunately (for PF_RING) the story is a…
For years, applications have used static ports so that port 80 means HTTP, and port 25 SMTP. Unfortunately this 1:1 mapping has been relaxed years ago with dynamic ports so that a…
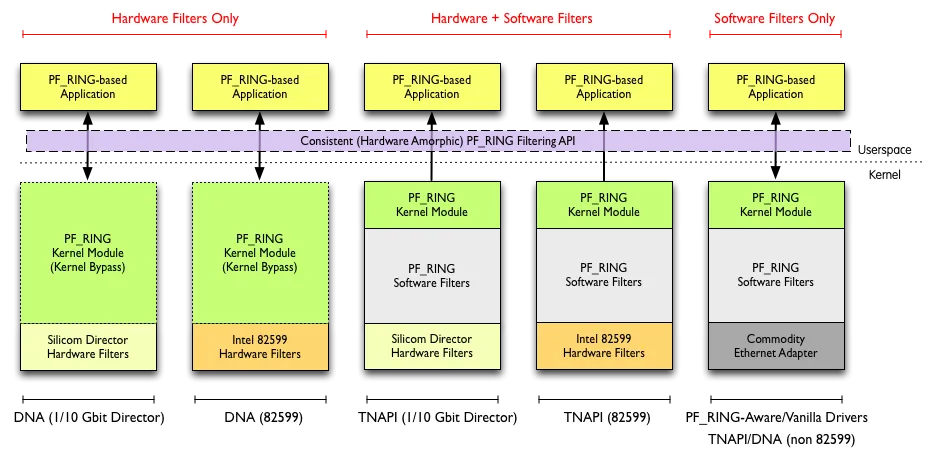
Introduction PF_RING filters have been designed to be efficient and versatile. PF_RING-based applications can use them for both reducing the amount of packets they need to process, and passing incoming packets to…
PF_RING 5.1 is a maintenance release that addresses some issues we identified in 5.0 that we released early this month. We have listen to your comments and tried to improve our software…